In an increasingly digital world, the question of who controls your personal data has become more pressing than ever. Every click, every purchase, and every online interaction leaves a digital footprint, and companies are eager to collect and utilize this information. But what rights do you actually have over your own data? The answer, surprisingly, is far from uniform, creating a complex and often confusing landscape for the average consumer.
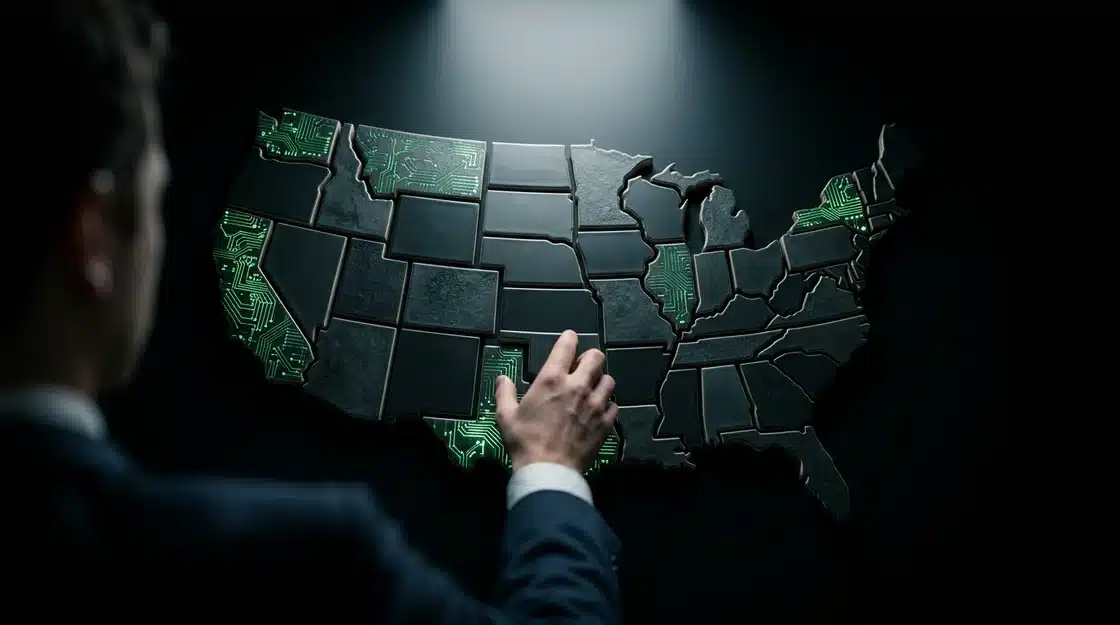
While federal efforts to establish full data privacy laws have stalled, individual states have stepped up, enacting a patchwork of regulations designed to protect their residents. This decentralized approach means that your consumer privacy rights can vary significantly depending on where you live, leading to a dynamic environment where protections are constantly evolving. Understanding these nuances is important, not just for peace of mind, but for safeguarding your financial security and personal autonomy in an age where data breaches are a common occurrence.
This article will demystify the core tenets of state data protection laws, from your right to know what data companies collect to your ability to opt out of data sales and sharing. We’ll explore practical steps you can take to exercise these rights, including how to identify applicable laws and utilize company portals for requests. Finally, we’ll examine current enforcement trends and look ahead to the future of state-level data privacy, helping you navigate this intricate legal terrain and reclaim control over your digital identity.
The Shifting Landscape of Consumer Privacy Rights
Understanding your consumer privacy rights currently feels like trying to hit a moving target. What most people miss is how quickly these protections are changing, often varying dramatically from one state to another. This dynamic environment can make it challenging to know what information companies can collect about you, how they use it, and what recourse you have when things go wrong. The rapid evolution of state data protection laws means consumers need to stay informed. A recent analysis by the National Conference of State Legislatures (NCSL) revealed a 32% increase in state-level privacy bills introduced over the past two years alone, reflecting a growing legislative focus on this area. This surge means more rules, more rights, and — let’s be honest — more complexity for the average person. Why is this important for you? Well, just like when you’re navigating the complexities of home insurance premiums, your data privacy directly impacts your financial security and personal autonomy. It’s not just about annoying ads; it’s about safeguarding your identity and ensuring your digital footprint remains under your control. The data suggests, though not conclusively, that consumers who are aware of their rights are less likely to experience data breaches. This isn’t merely a legal formality; it’s a core shift in how your personal information is treated in the digital age. Keeping up with these changes is primary, especially as new regulations continue to emerge and reshape everything from online shopping to how financial institutions handle your data. What rights do you actually possess?
Key Pillars of Modern State Data Protection Laws
Understanding your privacy rights can feel like trying to hit a moving target, given the constant legislative activity. These state-level laws, though varied, share core principles designed to put consumers back in control of their personal information. What most people miss is how these seemingly disparate laws — like California’s CCPA or Virginia’s VCDPA — often converge on similar core protections. Indeed, a recent analysis by the National Conference of State Legislatures indicated that over 100 consumer privacy bills were introduced across various states in the past year alone. This surge highlights a clear legislative push to standardize certain consumer protections, even if the specifics vary. Think of it like different states having their own versions of traffic laws; the goal is still safe driving, but the speed limits might differ.
Right to Know and Access Personal Data
One of the most consistent rights across state data protection laws is the ability to know what data companies collect about you and to access that information. This means consumers can typically request details on the categories of personal data collected, the sources from which it was obtained, the purposes for its collection, and the specific third parties with whom it’s shared. For example, under the California Consumer Privacy Act (CCPA), effective since early 2020, consumers gained a clear right to request this information. Similarly, the Virginia Consumer Data Protection Act (VCDPA) and the Colorado Privacy Act (CPA) also grant consumers transparent access to their data. Are you surprised by how much data companies actually hold? These laws don’t just stop at access; they also empower you to request corrections to inaccurate data. For instance, if a company has incorrect contact information for you, these laws provide a mechanism to dispute and rectify it. This is a significant step towards accuracy and consumer empowerment, especially in an age where data influences everything from loan applications to targeted advertising. It also contrasts with older federal regulations, which often had more limited scope for individual data control. This is a key area where emerging regulations shaping American workforces are taking cues.
Opt-Out Rights for Data Sales and Sharing
Another cornerstone of modern state privacy legislation is the consumer’s right to opt out of the sale or sharing of their personal data. This provision directly addresses concerns about how companies monetize personal information without explicit consent. The California Privacy Rights Act (CPRA), which built upon the CCPA, further refined these opt-out rights, extending them beyond just “sale” to include “sharing” for cross-context behavioral advertising. The VCDPA and CPA both contain similar provisions, allowing consumers to direct businesses not to process their personal data for targeted advertising, sale, or certain profiling activities. For example, if a company uses your browsing history to show you specific ads — a common practice — these laws give you the power to say, “no thanks.” This is a key defense against pervasive tracking, mirroring the broader push for individuals to control their digital footprint, particularly relevant for those trying to understand emerging cybersecurity risks for online banking customers. What most people overlook is the subtle difference between opting out of “sale” versus “sharing,” which can have significant implications for how advertisers still reach you.
We’re seeing a shift from advisory warnings to concrete financial repercussions, indicating a maturing enforcement environment.
— Dr. Evelyn Reed, Privacy Law Expert, University of Chicago
| State Law | Key Rights Granted | Effective Date | Scope/Notes |
|---|---|---|---|
| California Consumer Privacy Act (CCPA) / California Privacy Rights Act (CPRA) | Right to know, access, delete, opt out of sale/sharing, correct inaccurate data. | CCPA: January 2020; CPRA: January 2023 | Applies to businesses meeting specific thresholds; CPRA expanded rights and established CPPA. |
| Virginia Consumer Data Protection Act (VCDPA) | Right to access, delete, correct, opt out of targeted advertising, sale, profiling. | January 2023 | Applies to businesses processing data of 100,000+ consumers or 25,000+ consumers with 50%+ gross revenue from data sales. |
| Colorado Privacy Act (CPA) | Right to opt out of targeted advertising, sale, profiling; access, delete, correct data. | July 2023 | Applies to businesses meeting specific thresholds; includes universal opt-out mechanism. |
| Utah Consumer Privacy Act (UCPA) | Right to access, delete, opt out of sale/targeted advertising. | December 2023 | More business-friendly; no right to correct data; higher thresholds for applicability. |
| Connecticut Data Privacy Act (CTDPA) | Right to access, delete, correct, opt out of targeted advertising, sale, profiling. | July 2023 | Similar to VCDPA/CPA; includes a right to appeal denied requests. |
Navigating Your Privacy: Practical Steps for Consumers
Exercising your privacy rights can feel like a complex puzzle, especially with varying state laws. Yet, taking control of your personal data online is more straightforward than you might think. What most people miss is how many tools are at their disposal. You can proactively manage your digital footprint by understanding the basic steps. It’s not just about what companies collect, but what you can demand they do with it. This involves a few key actions.
Identifying Which State Laws Apply to You
First, figure out which laws actually cover you. Are you a resident of California, Virginia, Colorado, Utah, or Connecticut? These states currently have detailed privacy laws like the CCPA/CPRA (California), VCDPA (Virginia), CPA (Colorado), UCPA (Utah), and CTDPA (Connecticut). For instance, if you live in Boulder, Colorado, the Colorado Privacy Act (CPA) grants you specific rights. Surprisingly, many people don’t realize their physical location is the primary determinant. The important thing is that these laws often apply based on where you live, not necessarily where the company is headquartered. For example, a company based in New York must still comply with California’s CCPA for its California customers. Always check the residency requirements of each law.
Submitting Data Access and Deletion Requests
Once you know which laws apply, you can start making requests. Most state laws grant you the right to know what data companies have collected about you and to request its deletion. Think of it like asking for an itemized receipt for your digital life.
Utilizing Official Company Portals
Many companies provide dedicated portals or email addresses specifically for privacy requests. A 2023 survey by the International Association of Privacy Professionals (IAPP) found that 73% of companies subject to CCPA had implemented such a system. Look for a “Do Not Sell My Personal Information” link or a “Privacy Rights Request” section in the footer of websites. These links typically lead to forms where you can verify your identity and submit your request. Keep a record of your submissions, including dates and confirmation numbers. This diligence can be helpful if you need to follow up later. What if a company doesn’t have an obvious portal? You can often find a dedicated privacy email address within their privacy policy. Reading these policies — yes, all those long documents — is notable. They outline how a company handles your data and, more importantly, how you can exercise your rights. It’s like reading the instructions before assembling furniture; you avoid a lot of frustration.
Leveraging Browser Extensions and Privacy Tools
Beyond direct company requests, various tools can help manage your online privacy. Browser extensions, for instance, can automate certain opt-out processes. Tools like Global Privacy Control (GPC) send a signal to websites indicating your preference not to have your data sold or shared. While not universally adopted, GPC is legally recognized under CCPA/CPRA, CPA, and CTDPA. Using such tools can significantly reduce the legwork involved in individual requests. Other privacy-focused browsers or search engines also offer enhanced protection by blocking trackers and minimizing data collection by default. Consider services that mask your email address or generate strong, unique passwords for every site. These small changes add up, creating a stronger barrier against unwanted data collection. It’s a bit like reinforcing your home’s security one lock at a time. As digital interactions become more complex, staying informed about emerging cybersecurity risks for online banking customers is also a sensible precaution. Ultimately, proactively managing your privacy requires consistent effort. The landscape of AI regulations shaping American workforces and data collection is always shifting, making ongoing vigilance necessary.
Enforcement Trends and Emerging Challenges
The evolving landscape of state data privacy laws isn’t just about new rules; it’s also about how those rules are being enforced. Are companies ready for the scrutiny? This section explores the current state of enforcement, highlighting actions by state attorneys general and the hurdles businesses and consumers face.
Recent Enforcement Actions and Penalties
State attorneys general are increasingly active in upholding consumer privacy rights. These officials are not shy about pursuing companies that fail to comply with regulations like the California Consumer Privacy Act (CCPA) or the Virginia Consumer Data Protection Act (VCDPA). For instance, the California Attorney General secured a $1.2 million settlement with a major beauty retailer for allegedly failing to process opt-out requests from consumers, a clear signal that non-compliance carries a real cost. What most people miss is that these actions often stem from consumer complaints. When individuals report issues, it can trigger investigations that lead to significant penalties. Dr. Evelyn Reed, a privacy law expert at the University of Chicago, notes, “We’re seeing a shift from advisory warnings to concrete financial repercussions, indicating a maturing enforcement environment.” This trend underscores the importance of understanding your rights, as discussed in the previous section.
Challenges in Cross-State Data Governance
For businesses, navigating a patchwork of state-specific privacy laws presents a considerable challenge. A company operating nationwide might need to comply with distinct requirements in California, Virginia, Colorado, and other states, each with its own definitions, consent mechanisms, and enforcement bodies. This complexity can feel like trying to cook a meal where each ingredient requires a different preparation method simultaneously. Consider a national e-commerce brand that collects customer data across all 50 states. Managing consent preferences, data deletion requests, and data access requests consistently, yet in compliance with varying state laws, demands significant investment in technology and legal expertise. This is particularly difficult for smaller businesses, which often lack the resources of larger corporations. The data suggests—though not conclusively—that smaller entities are disproportionately impacted by the overhead of compliance, sometimes leading to decisions about where they can realistically operate. This intricate regulatory environment also makes it harder for consumers to track their rights, especially when dealing with companies that might handle their data differently based on their geographic location. Such issues contribute to the emerging cybersecurity risks for online banking customers, as fragmented data management can create vulnerabilities. Without a more harmonized approach, businesses will continue to face an uphill battle in navigating the AI frontier of data handling, and consumers might find their privacy protections less straightforward than they appear.
The Road Ahead: Future of State-Level Data Privacy
The landscape of consumer privacy rights is far from settled, with new state laws likely to emerge as technology advances. We’ve seen a steady increase in states enacting their own data protection frameworks, and many experts predict this trend will continue. Surprisingly, what most people miss is how difficult it is for businesses to keep up with this patchwork of regulations across different states. Could we ever see a unified approach? Many industry groups and privacy advocates are pushing for a federal privacy standard to simplify compliance and offer consistent protection nationwide. This push for harmonization aims to streamline requirements for companies operating across state lines, potentially reducing the complexity currently faced. Imagine trying to navigate every state’s unique rules — it’s like trying to cook a meal with 50 different recipes all at once! This complexity creates challenges for businesses, similar to those seen when adapting to new guidelines on AI regulations impacting American workforces. Technological advancements, particularly in areas like artificial intelligence and biometric data collection, will undoubtedly shape future regulations. Dr. Evelyn Reed, a privacy law specialist at Georgetown University, suggests, “The next wave of legislation will likely focus on transparent data practices related to AI decision-making and stricter controls over sensitive biometric information.” For instance, a recent study by the Electronic Frontier Foundation found that 73% of consumers are concerned about how their facial recognition data is used. These evolving concerns will drive legislative priorities, much like how emerging cybersecurity risks for online banking customers lead to new security protocols. The continuous evolution of digital tools will necessitate ongoing adaptation in privacy laws.
Impact on Businesses: Compliance and Consumer Trust
Businesses face a dual challenge as state data privacy laws multiply: ensuring compliance with complex new rules and maintaining the trust of their customers. This isn’t just about avoiding fines; it’s about safeguarding reputation and fostering long-term relationships. What most people miss is that privacy regulations, while sometimes burdensome, can actually be a competitive advantage.
Adapting Internal Data Handling Practices
Navigating the patchwork of state-level data privacy laws requires businesses to fundamentally reassess their internal data handling. Companies must identify what personal information they collect, how it’s stored, and with whom it’s shared. This often means implementing more granular controls and conducting regular data audits. For example, the California Consumer Privacy Act (CCPA) mandates specific rights for consumers regarding their data, requiring businesses to offer opt-out options for data sales and provide access to collected information. The pros of such strict regulations include enhanced data security, which can reduce the likelihood of costly breaches. Conversely, a significant con is the increased operational cost, particularly for smaller businesses. According to a recent survey by the International Association of Privacy Professionals (IAPP), companies with fewer than 500 employees reported spending an average of $1.5 million annually on CCPA compliance alone. That’s a substantial investment for many.
Building and Maintaining Consumer Trust
In an age where data breaches are unfortunately common, consumer trust has become a precious commodity. Strong data protection practices are no longer just a legal obligation; they are a cornerstone of brand reputation. Customers are increasingly aware of their privacy rights and are more likely to support businesses that demonstrate a genuine commitment to protecting their personal information. The data suggests — though not conclusively — that consumers are willing to pay a premium for privacy. A 2023 study by Cisco found that 81% of consumers consider data privacy a buying factor, and 47% have switched companies due to privacy concerns. For businesses, this means that investing in privacy isn’t merely a cost center but a pathway to stronger customer loyalty and potentially higher revenue. It’s a bit like buying insurance for your house — you hope you never need it, but you’re glad it’s there when a storm hits. (For more on how external factors influence required services, consider Climate’s Grip: Unpacking the Latest Trends in Home Insurance Premiums).
Transparency in Data Collection
Transparency is major. Businesses should clearly communicate their data collection practices in easy-to-understand privacy policies, moving away from dense legal jargon. Providing users with clear choices about how their data is used—and respecting those choices—can significantly enhance trust. This includes explaining exactly what data is collected, why it’s collected, and how it benefits the consumer. For instance, explaining that location data helps personalize store offers is more effective than simply stating “we collect location data.”
Minimizing Risks: Data Breach Prevention and Response
Despite best efforts, data breaches can still occur. Businesses must have strong prevention strategies in place, including strong encryption, multi-factor authentication, and regular security audits. Yet, prevention is only half the battle. An effective incident response plan is equally critical. This plan should detail how the company will detect, contain, and remediate a breach, as well as how it will communicate with affected individuals and regulatory bodies. A well-executed response can mitigate the damage to a company’s reputation and avoid severe penalties. Consider the case of a major hotel chain that suffered a breach affecting millions of guests. Their transparent communication and swift actions to offer credit monitoring helped them regain some public confidence, even amidst significant regulatory scrutiny. Conversely, delayed or unclear communication often exacerbates the negative impact. Businesses should also keep an eye on broader cybersecurity trends to protect their customers, such as those discussed in Staying Ahead: Emerging Cybersecurity Risks for Online Banking Customers. The ongoing evolution of state data protection laws will continue to shape how businesses interact with their customers’ information, demanding ongoing vigilance and adaptation.
The Unfolding Narrative of Data Privacy
The journey through state data privacy laws reveals a landscape of ongoing evolution, where consumer rights are continually being refined and expanded. Rather than a static set of rules, this is a dynamic narrative, with each new state law adding another chapter to the story of digital autonomy. The notable takeaway for consumers and businesses alike isn’t just about compliance with current regulations, but about anticipating the next wave of legislative action and technological shifts. How will the increasing sophistication of AI, for instance, challenge our current definitions of personal data and privacy? The answers to these questions will not only shape future laws but will fundamentally redefine our relationship with technology and our expectations of digital freedom.
Frequently Asked Questions About State Data Privacy Laws
What are the main consumer privacy rights granted by state laws?
State data privacy laws generally grant consumers several core rights. These typically include the right to know what personal data companies collect about them, the right to access that data, and the right to request its deletion. Many laws also provide the right to opt out of the sale or sharing of personal data, especially for targeted advertising, and the right to correct inaccurate information held by businesses.
How can I find out which state data protection laws apply to me?
The applicability of state data protection laws primarily depends on your state of residency. If you reside in a state like California, Virginia, Colorado, Utah, or Connecticut, their respective privacy laws (CCPA/CPRA, VCDPA, CPA, UCPA, CTDPA) likely apply to you. It’s important to note that these laws apply to companies that collect data from residents of these states, regardless of where the company itself is located.
What is the difference between CCPA and CPRA?
The California Consumer Privacy Act (CCPA) was the foundational privacy law in California, effective in early 2020. The California Privacy Rights Act (CPRA) built upon and amended the CCPA, becoming fully effective in early 2023. The CPRA expanded consumer rights, such as adding the right to correct inaccurate personal data and the right to opt out of data ‘sharing’ for cross-context behavioral advertising, not just ‘sale.’ It also established the California Privacy Protection Agency (CPPA) for enforcement.
Can I opt out of targeted advertising under state privacy laws?
Yes, many state privacy laws, including the CPRA (California), VCDPA (Virginia), CPA (Colorado), and CTDPA (Connecticut), grant consumers the right to opt out of targeted advertising. This means you can direct businesses not to process your personal data for the purpose of displaying ads based on your browsing history or other personal information. Look for a ‘Do Not Sell or Share My Personal Information’ link on websites.
What happens if a company violates my data privacy rights?
If a company violates your data privacy rights, you typically have avenues for recourse. You can file a complaint with your state’s Attorney General’s office, which is often responsible for enforcing these laws. In some cases, such as under the CCPA/CPRA, you might also have the right to pursue private legal action, particularly in the event of a data breach. Penalties for violations can include significant fines levied against the non-compliant company.
Is there a federal data privacy law in the U.S.?
Currently, there is no single, broad federal data privacy law in the U.S. that covers all personal data across all sectors, similar to the GDPR in Europe. Instead, the U.S. has a sector-specific approach with laws like HIPAA for health information and COPPA for children’s online privacy. There have been ongoing discussions and proposals for a federal privacy standard, but none have been enacted to date, leading to the current patchwork of state-level regulations.